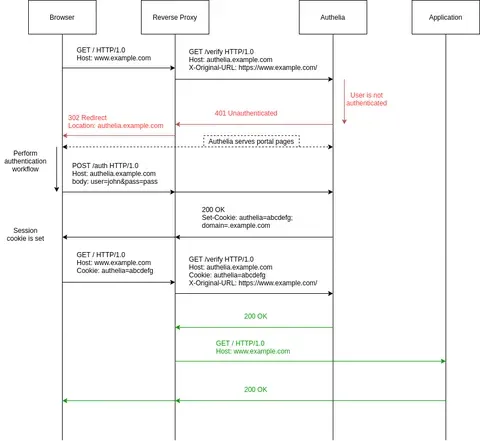
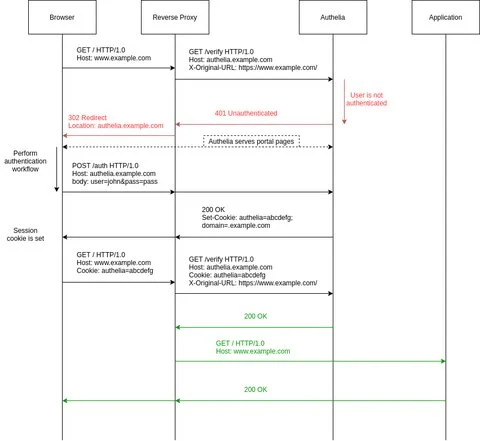
Authelia must be integrated with a compatible reverse proxy for proxy-based application protection.
The buyer must operate and configure both components, including forwarding the expected request headers.
Evidence source ↗
Authelia is open-source, self-hosted identity software that adds authentication and access policies to web applications through a reverse proxy. It supports MFA, SSO, LDAP or file-based users, and an OpenID Connect provider.
Documentation verifies MFA, proxy-based access policies, LDAP and file authentication, and an OpenID Connect provider. Self-hosting avoids a software subscription but requires configuration and ongoing administration. No reliable public review scores or review themes were verified.
This profile combines documented product information and independent evidence where available. It is not a hands-on test unless TechZella explicitly identifies one.
A quick way to understand who this product may suit, where its limits matter, and which facts are most relevant before you compare alternatives.
Technically capable teams and self-hosters that operate a reverse proxy and want centralized authentication, MFA, and access rules for web applications.
Buyers seeking a managed identity service, a credential vault, or a supported enterprise directory with provisioning and lifecycle automation should assess other products. Authelia is self-hosted, and its OpenID Connect provider is documented as open beta, and should evaluate alternatives such as Authentik or Keycloak instead.
Docker, Kubernetes, Linux, Self-hosted, Web
7.0/10
Authelia is an open-source identity and access service for web applications. It works with a reverse proxy, which sends authorization requests to Authelia before allowing users to reach protected services.
It supports first-factor authentication through LDAP or a local user file, along with second-factor methods and access policies. It is not a password-manager vault: its password functions concern account authentication, changes, and resets.
These are the product-specific differences that may matter when deciding whether the software fits your workflow. They are based on documented evidence rather than a universal ranking.
These are documented constraints or practical friction points that may matter before you adopt the product.
The buyer must operate and configure both components, including forwarding the expected request headers.
Evidence source ↗Teams should verify client compatibility and beta suitability before making it a dependency for production sign-in.
Evidence source ↗Unplanned automatic upgrades may require configuration or migration work.
Evidence source ↗No software subscription or trial was found. Hosting, configuration, maintenance, and support are operator responsibilities.
Check current pricing →Pricing may change. Verify current plans on the vendor's website.
Compare similar products directly, then see which alternatives may make more sense when your requirements differ.
These products address broadly similar requirements. The descriptions focus on documented reasons a buyer might compare them with Authelia.

| License and pricing | Open-source software; project reports no monetization model |
|---|---|
| Deployment | Self-hosted; Docker, Kubernetes, standalone packages and binaries |
| Authentication backends | LDAP or local file |
| Storage | SQLite, MySQL, PostgreSQL |
| Reverse proxy support | Traefik, Caddy, Envoy, NGINX, HAProxy, and others; support varies |
| API | HTTP proxy authorization and OpenID Connect endpoints; no general-purpose admin REST API verified |
| Free trial | Not applicable; software is free to deploy |
| Identity lifecycle | No internal user registration; external registration service can be linked |
| OpenID Connect status | Provider role documented as open beta; relying-party role unsupported |
Verified installation, hosting, administration, or environment details that can affect implementation.
| Hosting | Self-hosted service, deployable with Docker, Kubernetes, or supported standalone packages and binaries. Source ↗ |
|---|---|
| Authentication backend | LDAP directory or a local file with user records and hashed passwords. Source ↗ |
| Persistent storage | Local SQLite, MySQL, or PostgreSQL storage can hold user preferences, second-factor data, and authentication logs. Source ↗ |
Documented portability, standards, export, or switching considerations. No switching-cost score is shown unless the evidence supports one.
Authelia can use an existing LDAP directory or a file-based user database. The documentation does not establish a general migration service for moving users from another identity product.
Evidence source ↗Authelia automatically checks and upgrades its storage schema on startup; downgrading may require a supported manual schema downgrade.
Evidence source ↗A proprietary editorial score based on product capabilities, usability, value, performance, support and user sentiment evidence.
Documentation verifies MFA, proxy-based access policies, LDAP and file authentication, and an OpenID Connect provider. Self-hosting avoids a software subscription but requires configuration and ongoing administration. No reliable public review scores or review themes were verified.
Methodology v1.0. The assessment weighs feature coverage (25%), ease of use (15%), value for money (20%), performance (15%), support (10%) and user sentiment (15%), using researched product evidence and verified review evidence where available. It is a TechZella editorial assessment, not a direct user-review average.
Key claims are linked to the sources used to verify them. This evidence record is separate from third-party user ratings.
TechZella evaluates software using documented product capabilities, pricing information, usability and value considerations, independent user evidence where available, and competitive context. The assessment is an editorial review, not a hands-on test unless one is explicitly identified. Our editorial assessment is based on 6 documented sources.
The project describes its role as providing MFA and SSO for applications through a web portal and companion reverse-proxy workflow.
View source ↗Verified 2026-10-08The authentication documentation identifies LDAP directories and a local YAML user file with hashed passwords as backend choices.
View source ↗Verified 2026-10-08The provider documentation states both its beta status and that Authelia does not support acting as an OpenID Connect relying party.
View source ↗Verified 2026-10-08The proxy support table lists Traefik, Caddy, Envoy, NGINX, HAProxy, and other implementations, with support varying by feature and deployment context.
View source ↗Verified 2026-10-08The project's about page describes its volunteer contributors and says it is not a company or incorporated entity.
View source ↗Verified 2026-10-08Its integration guide documents endpoints and configuration for OpenID Connect clients, including a WordPress example.
View source ↗Verified 2026-10-08No reviews yet. Be the first to share your experience.
Please log in to submit a review.
Is Authelia a password manager? No. It authenticates users and applies access policies; it does not function as a vault for storing and autofilling website credentials.
Does it support LDAP and Active Directory? Yes. Its LDAP backend documentation includes Active Directory among directory options.
Does Authelia have an API? It documents HTTP authorization endpoints for reverse proxies and OpenID Connect endpoints for clients. This should not be confused with a general-purpose administrative REST API.
Can it run in Docker or Kubernetes? Yes. The project documents Docker deployment and supports Kubernetes-oriented deployment options, with some Helm material identified as beta.
Is there a free trial? No trial is listed because the software is free and self-hosted. Users can deploy it themselves.