Iris Investigate access is provisioned through a DomainTools Enterprise account.
Teams should confirm account authorization, API entitlement, and pricing with DomainTools before planning a rollout.
Evidence source ↗
DomainTools Iris is a domain-intelligence platform for investigating internet infrastructure, assessing domain risk, and enriching security workflows through web tools, APIs, and integrations.
Official documentation verifies investigation, enrichment, detection, API access, and security-platform integrations. Public product-specific review evidence and published prices were not verified, limiting value and sentiment assessments.
This profile combines documented product information and independent evidence where available. It is not a hands-on test unless TechZella explicitly identifies one.
A quick way to understand who this product may suit, where its limits matter, and which facts are most relevant before you compare alternatives.
Security operations teams and threat investigators that need to examine domain infrastructure, pivot across connected identifiers, and feed domain intelligence into established SIEM or SOAR workflows.
Buyers seeking a general-purpose web-scraping product, or individuals seeking a self-serve commercial Iris Investigate subscription, should look elsewhere; the vendor describes Iris access as an Enterprise offering.
Cloud, REST API, SaaS, Web
7.0/10
DomainTools Iris is a domain-intelligence suite for security investigations and operational workflows. Its products divide into Iris Investigate for analyst-led domain and infrastructure research, Iris Enrich for adding domain context at scale, and Iris Detect for discovering and monitoring suspicious or lookalike domains.
Iris Investigate supports searches and pivots across domain, IP, email, registration, DNS, and certificate data. Its workspace includes investigation history and specialized data panels. DomainTools also documents APIs and connectors that bring Iris data into security tools.
The requested Web Scraping category is not a supported fit: the reviewed product material describes threat intelligence and domain investigation, not a general-purpose web scraping tool.
These are the product-specific differences that may matter when deciding whether the software fits your workflow. They are based on documented evidence rather than a universal ranking.
These are documented constraints or practical friction points that may matter before you adopt the product.
Teams should confirm account authorization, API entitlement, and pricing with DomainTools before planning a rollout.
Evidence source ↗Large result sets may need narrower queries or another supported workflow.
Evidence source ↗For security-sensitive software, TechZella focuses on documented architecture, authentication, data handling, deployment and privacy details that can affect a buying decision. This is product research, not an independent security audit.
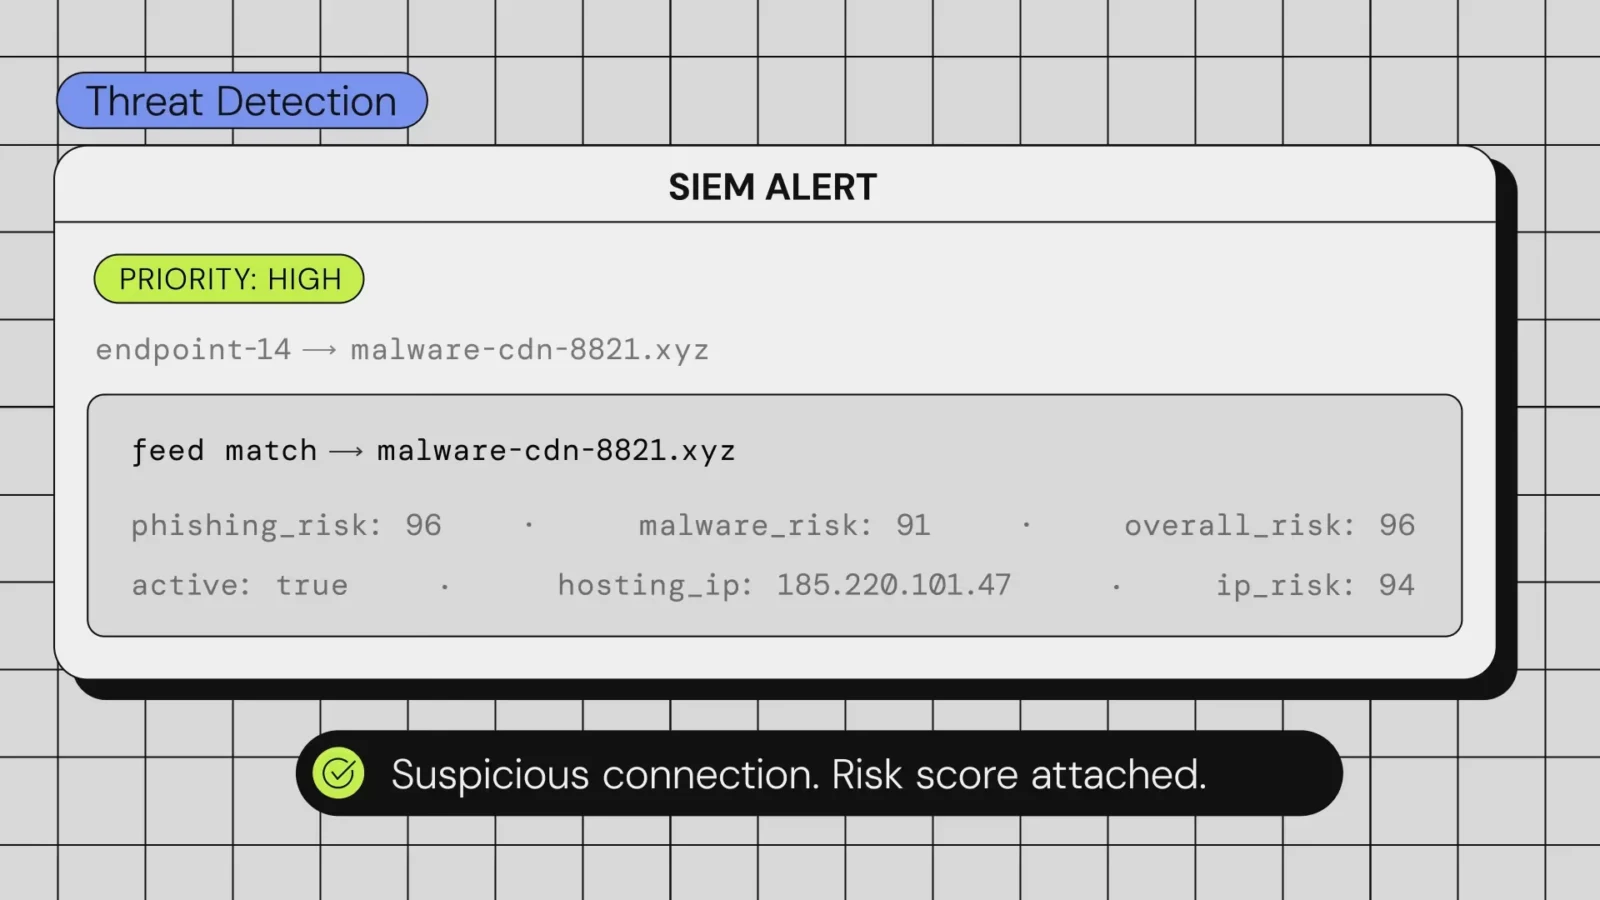
The integrations catalog maps DomainTools products and APIs to SIEM, SOAR, XDR, threat-intelligence, and investigation platforms.
Source ↗Security claims are presented only when supported by documented sources. The presence of this section does not constitute a penetration test, certification or independent security audit.
DomainTools lists Iris Investigate and Iris APIs among Enterprise capabilities. Contact DomainTools for pricing and access levels.
Check current pricing →Pricing may change. Verify current plans on the vendor's website.
DomainTools documents a Recorded Future integration that places Iris Investigate domain profiles in a Recorded Future Domain Intel Card. This is an adjacent workflow rather than a verified substitute comparison. Buyers comparing products should assess the coverage of domain and infrastructure data, investigation workflow, required integrations, API entitlements, and contract terms directly with vendors.
| Access | Enterprise account provisioning |
|---|---|
| Interface | Web application |
| API | REST APIs; API access requires authorized DomainTools account access |
| Free trial | No product trial verified; no-charge API test queries are available for configuration |
| Integrations | Documented connectors and workflows for selected security platforms, including Splunk, Microsoft Sentinel, Elastic, and ServiceNow |
Verified installation, hosting, administration, or environment details that can affect implementation.
| Installation or hosting | Iris Investigate is accessed through a web application. DomainTools also provides REST APIs and integrations; the reviewed sources do not document customer-managed on-premises installation of Iris itself. Source ↗ |
|---|
A proprietary editorial score based on product capabilities, usability, value, performance, support and user sentiment evidence.
Official documentation verifies investigation, enrichment, detection, API access, and security-platform integrations. Public product-specific review evidence and published prices were not verified, limiting value and sentiment assessments.
Methodology v1.0. The assessment weighs feature coverage (25%), ease of use (15%), value for money (20%), performance (15%), support (10%) and user sentiment (15%), using researched product evidence and verified review evidence where available. It is a TechZella editorial assessment, not a direct user-review average.
Key claims are linked to the sources used to verify them. This evidence record is separate from third-party user ratings.
TechZella evaluates software using documented product capabilities, pricing information, usability and value considerations, independent user evidence where available, and competitive context. The assessment is an editorial review, not a hands-on test unless one is explicitly identified. Our editorial assessment is based on 3 documented sources.
The product guide documents searching on domains and other identifiers, pivoting across connected data, and reviewing domain, passive DNS, WHOIS history, certificate, and visualization panels.
View source ↗Verified 2026-10-08DomainTools API documentation distinguishes these three APIs and describes their investigation, enrichment, and monitoring workflows.
View source ↗Verified 2026-10-08The API documentation says the Iris APIs are available as part of Enterprise accounts and directs organizations to contact DomainTools about pricing and access levels.
View source ↗Verified 2026-10-08The integrations catalog maps DomainTools products and APIs to SIEM, SOAR, XDR, threat-intelligence, and investigation platforms.
View source ↗Verified 2026-10-08The user guide directs users to access Iris Investigate through its web interface and explains organization-provisioned access.
View source ↗Verified 2026-10-08No reviews yet. Be the first to share your experience.
Please log in to submit a review.
Is DomainTools Iris a web-scraping tool?
No. The reviewed documentation describes domain threat intelligence, infrastructure investigation, enrichment, and monitoring.
Does Iris have an API?
Yes. DomainTools documents REST APIs for Iris Investigate, Iris Enrich, and Iris Detect. Access is associated with DomainTools Enterprise accounts.
What platforms does Iris integrate with?
Documented examples include Splunk, Microsoft Sentinel, Elastic, Google Chronicle, IBM QRadar, ServiceNow, Palo Alto Cortex, CrowdStrike, Anomali, MISP, and Maltego. Availability depends on the specific integration and account.
How much does Iris cost?
Public Iris pricing was not found. DomainTools directs organizations to contact it about Enterprise pricing and access.
Is there a free trial?
A product trial was not verified. The API guide provides no-charge test queries for configuration, which should not be treated as a full trial.
What is Iris Investigate best suited for?
It is suited to security analysts and threat hunters investigating suspicious domains and connected internet infrastructure.